GRC and Risk Compliance Services in UAE: How ISO Standards Build Your Framework
Boards and regulators now expect organisations to show control over governance, risk and compliance. GRC and risk compliance services in the UAE help you do this in a structured way, instead of managing policies, risks and audits in separate silos. This article explains what GRC means and how ISO management system standards turn it into daily practice.
What Is GRC?
- Governance: how decisions are made, who is accountable and how objectives are set.
- Risk: identifying, assessing and treating threats and opportunities.
- Compliance: meeting legal, regulatory, contractual and internal requirements.
Our Governance, Risk and Compliance services support organisations that want an integrated approach.
Why UAE Businesses Need GRC
- Growing regulation on data protection, anti-bribery, safety and environment.
- Customer and tender requirements for documented controls.
- Cyber and operational risks that affect continuity.
- Need for evidence during audits and due diligence.
How ISO Standards Support GRC
| GRC Need | Relevant ISO Standard |
|---|---|
| Quality governance | ISO 9001:2015 certification in UAE |
| Information security risk | ISO/IEC 27001:2022 certification in UAE |
| Privacy compliance | ISO/IEC 27701:2019 certification |
| Business continuity risk | ISO 22301:2019 business continuity certification |
| Health and safety compliance | ISO 45001:2018 certification in UAE |
| Environmental compliance | ISO 14001:2015 certification in UAE |
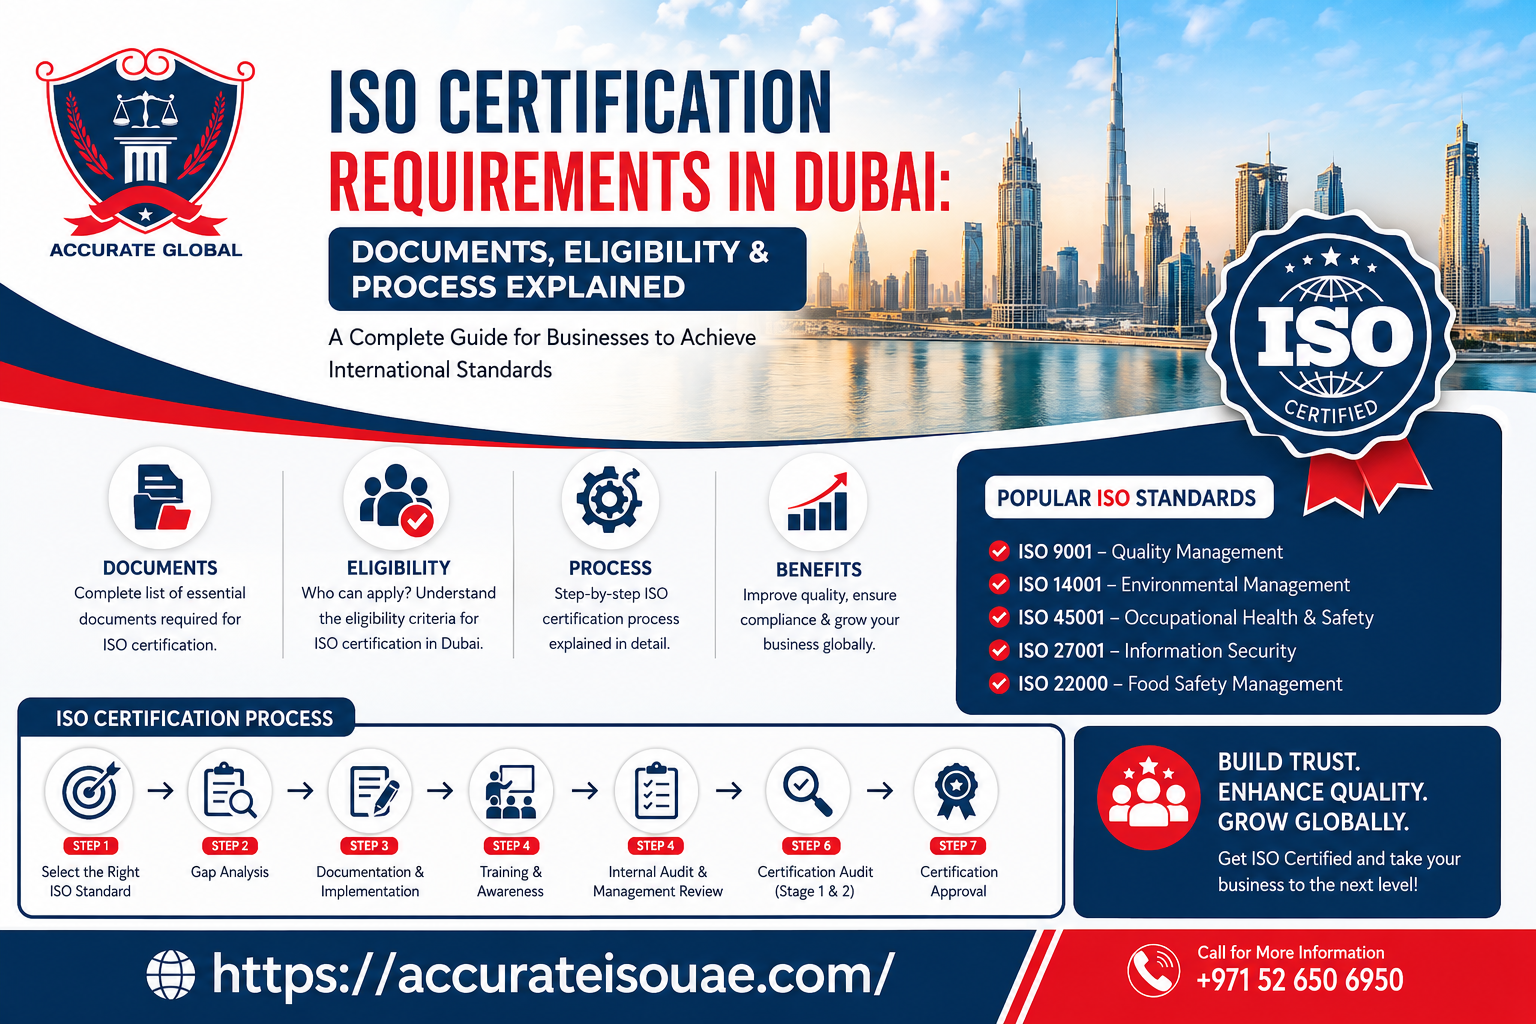
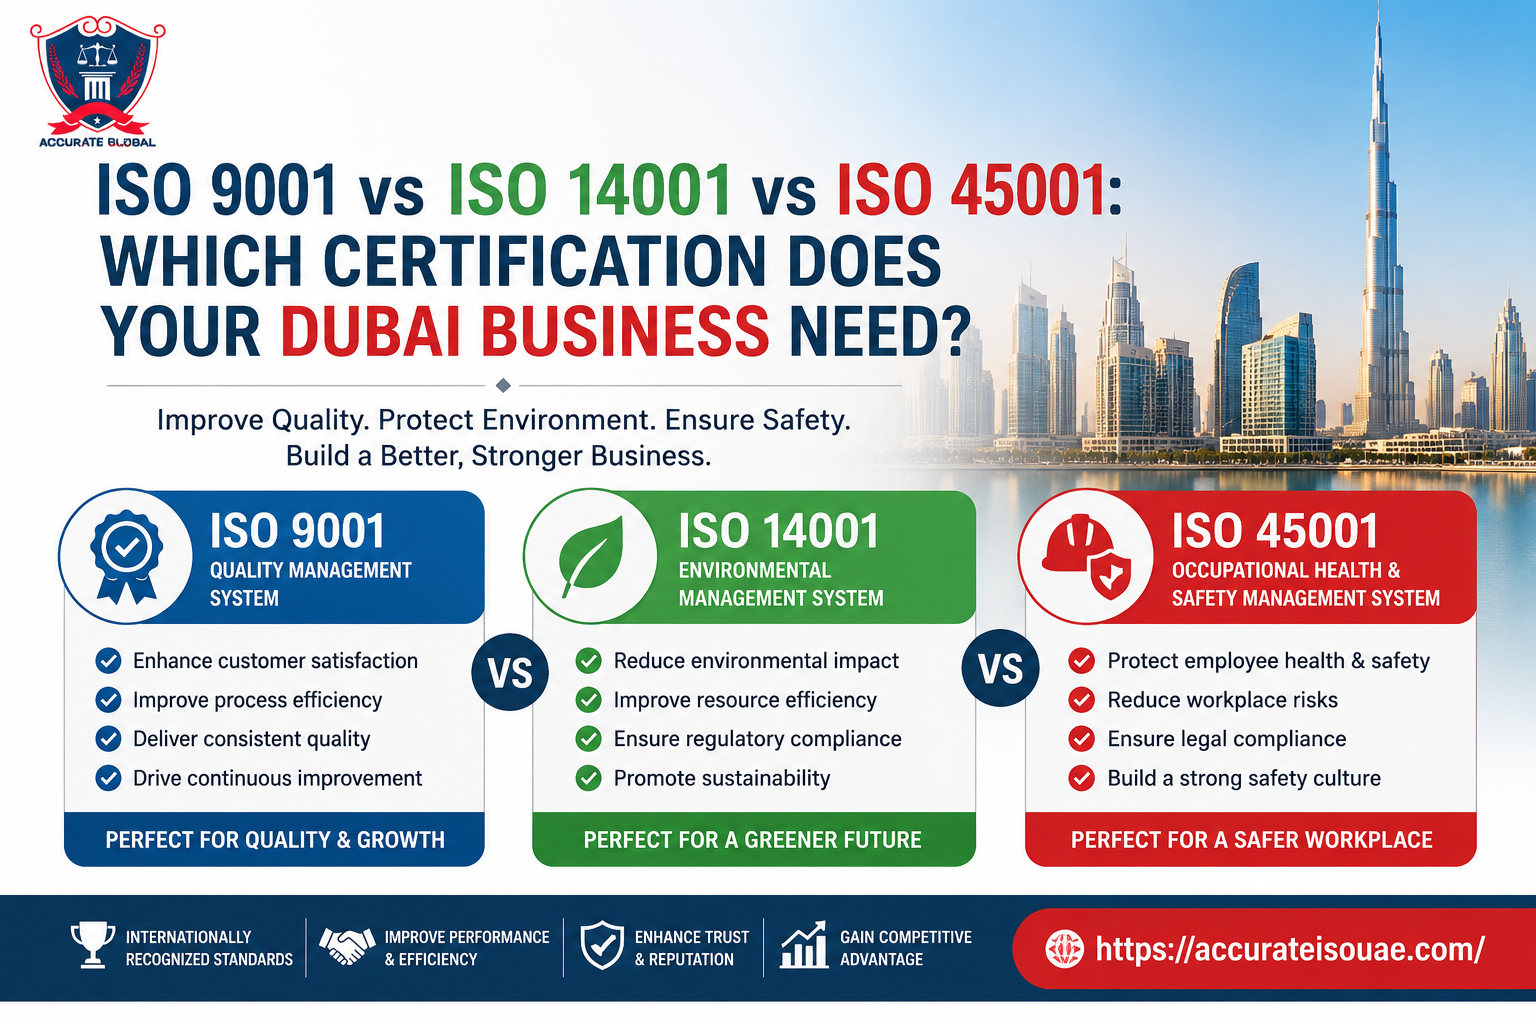
All of these share a common high-level structure, so you can integrate them into one management system and avoid duplicated work. Not sure which to start with? Read ISO 9001 vs ISO 14001 vs ISO 45001.
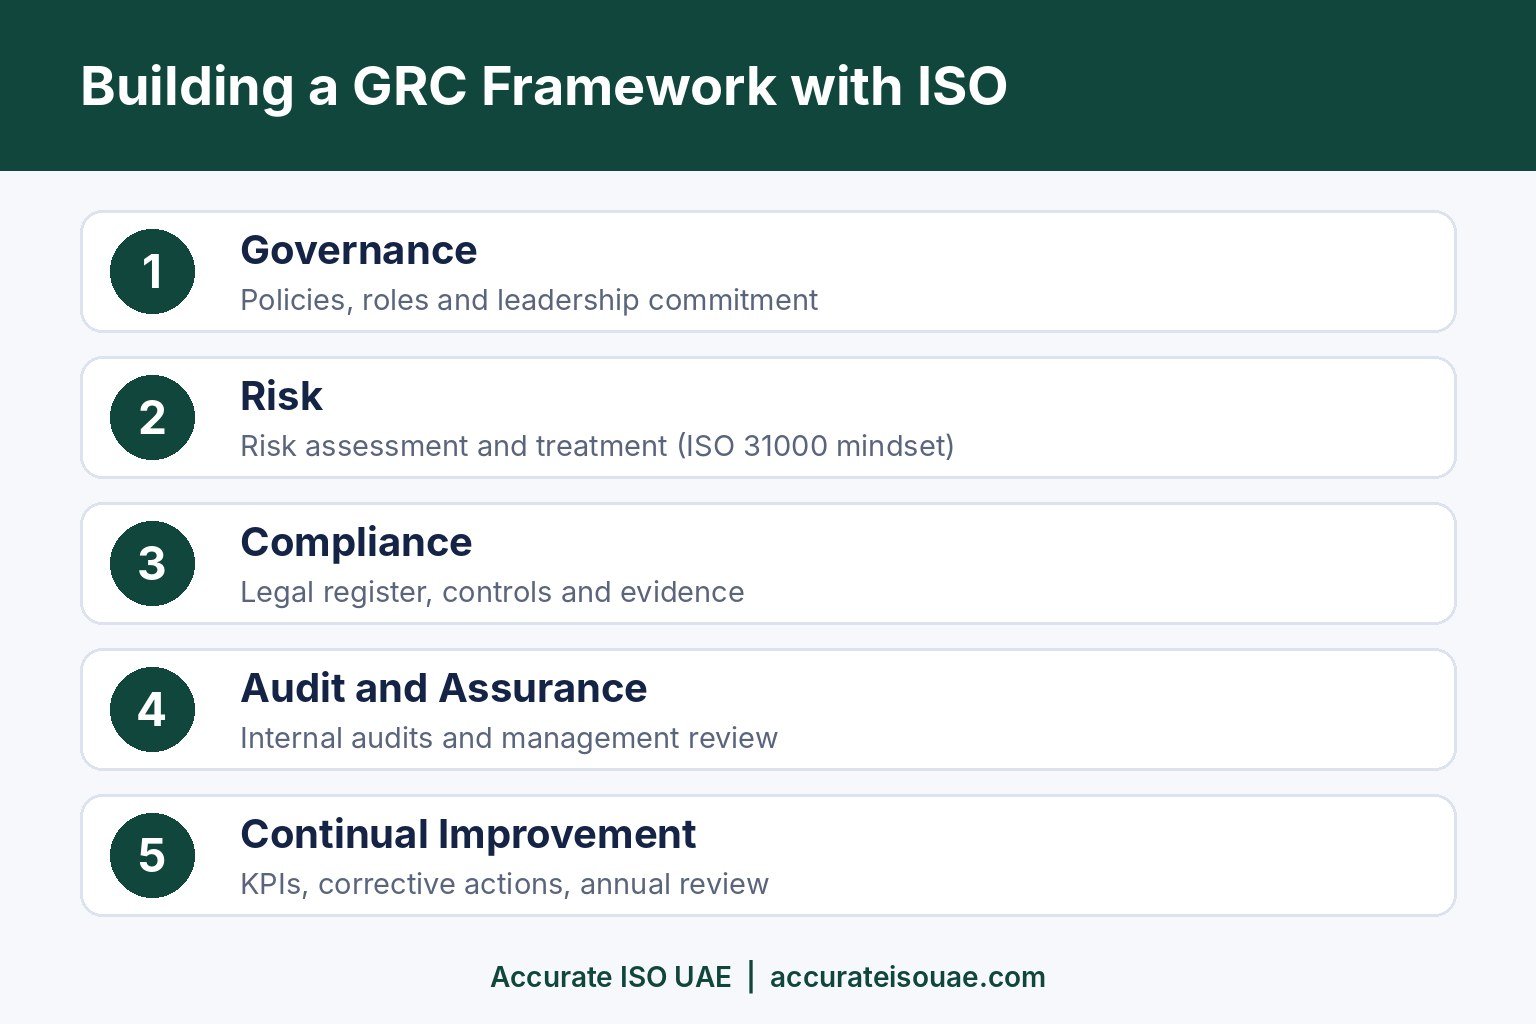
Building a Practical GRC Framework
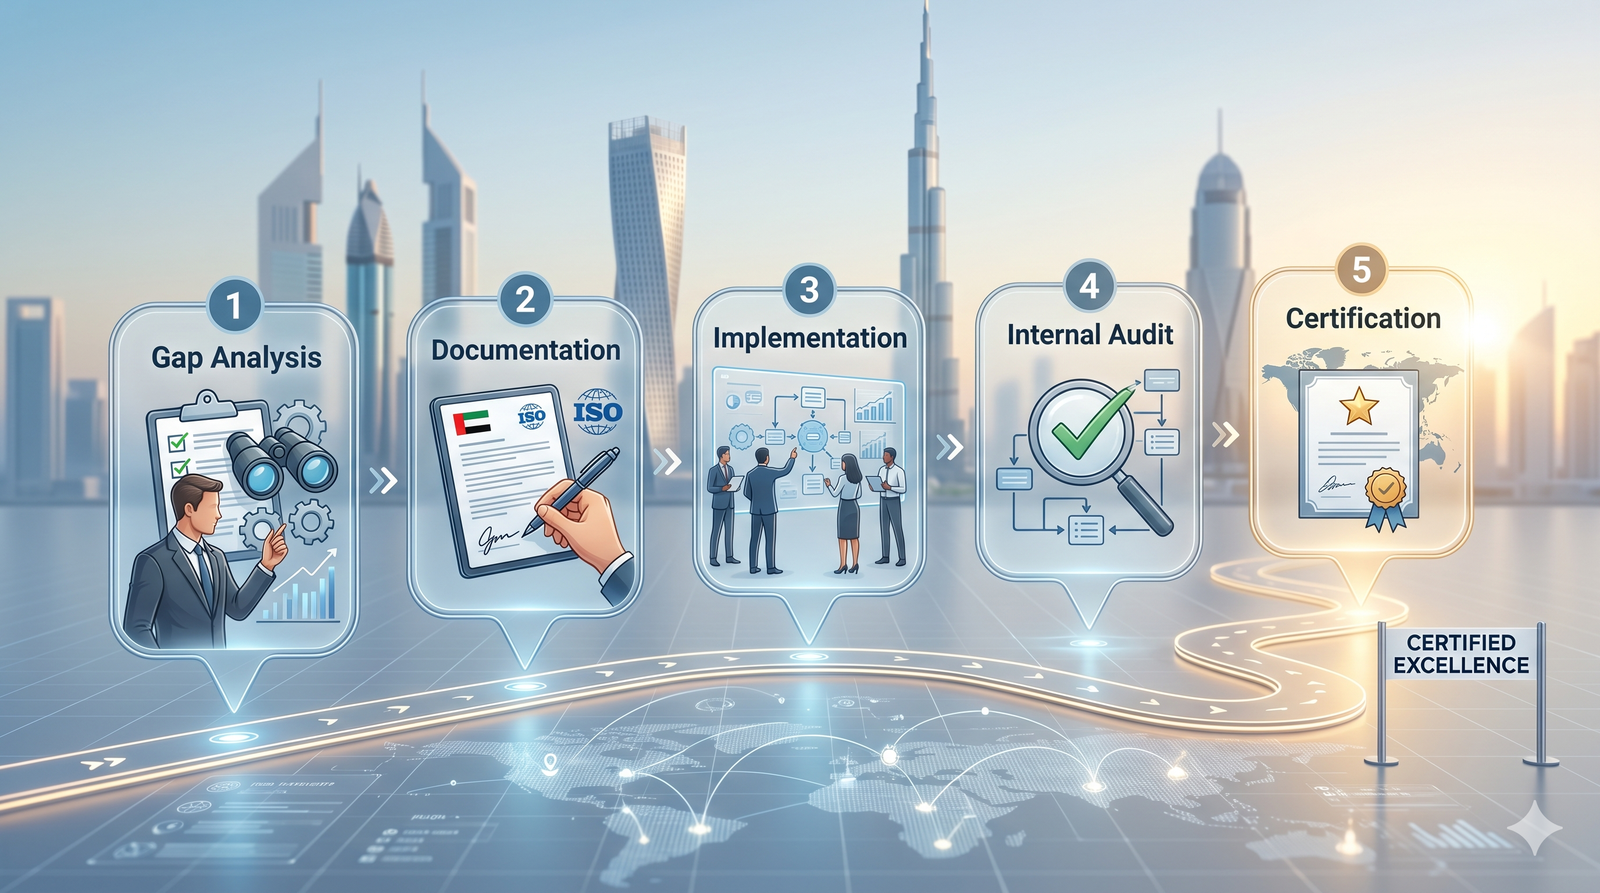
1. Governance
Set policies, assign roles and secure leadership commitment. Without it, controls are ignored.
2. Risk Management
Maintain a risk register, score risks consistently and assign treatment owners. Review it at least annually.
3. Compliance Register
List applicable laws, customer requirements and certifications, with owners and review dates.
4. Audit and Assurance
Run internal audits and management reviews to verify that controls work. Learn more in our Stage 1 and Stage 2 audit process article.
5. Continual Improvement
Track KPIs, close corrective actions and update the framework as the business changes.
GRC Training for Your Team
Tools alone do not create compliance. Teams need training in risk assessment, internal auditing and ISO requirements so that responsibilities are understood by everyone. Ask us about training options through our contact page.
Choosing a GRC Partner
- Experience in your industry and the UAE regulatory context.
- Clear deliverables: gap analysis, risk register, policies, training.
- Independence between advisory and certification.
- Support after implementation.
The same selection principles apply as in how to choose ISO consultants in UAE. For data security projects see ISO 27001 compliance in the UAE.
Frequently Asked Questions
What are GRC services?
GRC services help organisations align governance, risk management and compliance activities through policies, risk assessments, controls, training and audits.
Is GRC the same as ISO certification?
No. ISO certification is one proof of an effective management system, while GRC is the wider approach to governance, risk and compliance.
Which ISO standard is best for risk and compliance?
It depends on your risks. Many UAE firms start with ISO 9001 or ISO/IEC 27001 and add others over time.
Do you offer GRC training in Dubai?
Yes, we can discuss training and awareness programmes for your team. Contact us for details.
Get Expert Support
Looking for risk and compliance support in the UAE? Speak to our team for a free consultation: call +971 52 315 0586, email info@accurateiso.com or contact our team to request a quote. You can also review our ISO certification prices page to plan your budget.
.png)
.png)
.png)
.png)
.png)
.png)
.png)