ISO 27001 Compliance in the UAE: Controls, Gap Analysis and Audit Readiness
Customers, regulators and global partners increasingly ask UAE companies to prove how they protect data. ISO 27001 compliance in the UAE gives you a recognised, auditable way to do exactly that. This guide covers what the standard requires, how to run a gap analysis and how to prepare for the certification audit.
What Is ISO/IEC 27001:2022?
ISO/IEC 27001:2022 is the international standard for an Information Security Management System (ISMS). It requires you to identify information security risks, select controls and continually improve. The 2022 edition lists 93 controls in four themes: organisational, people, physical and technological. Our page on ISO/IEC 27001:2022 certification in UAE explains the service, and our ISO/IEC 27001:2022 certification guide gives a deeper overview.
Why It Matters in the UAE
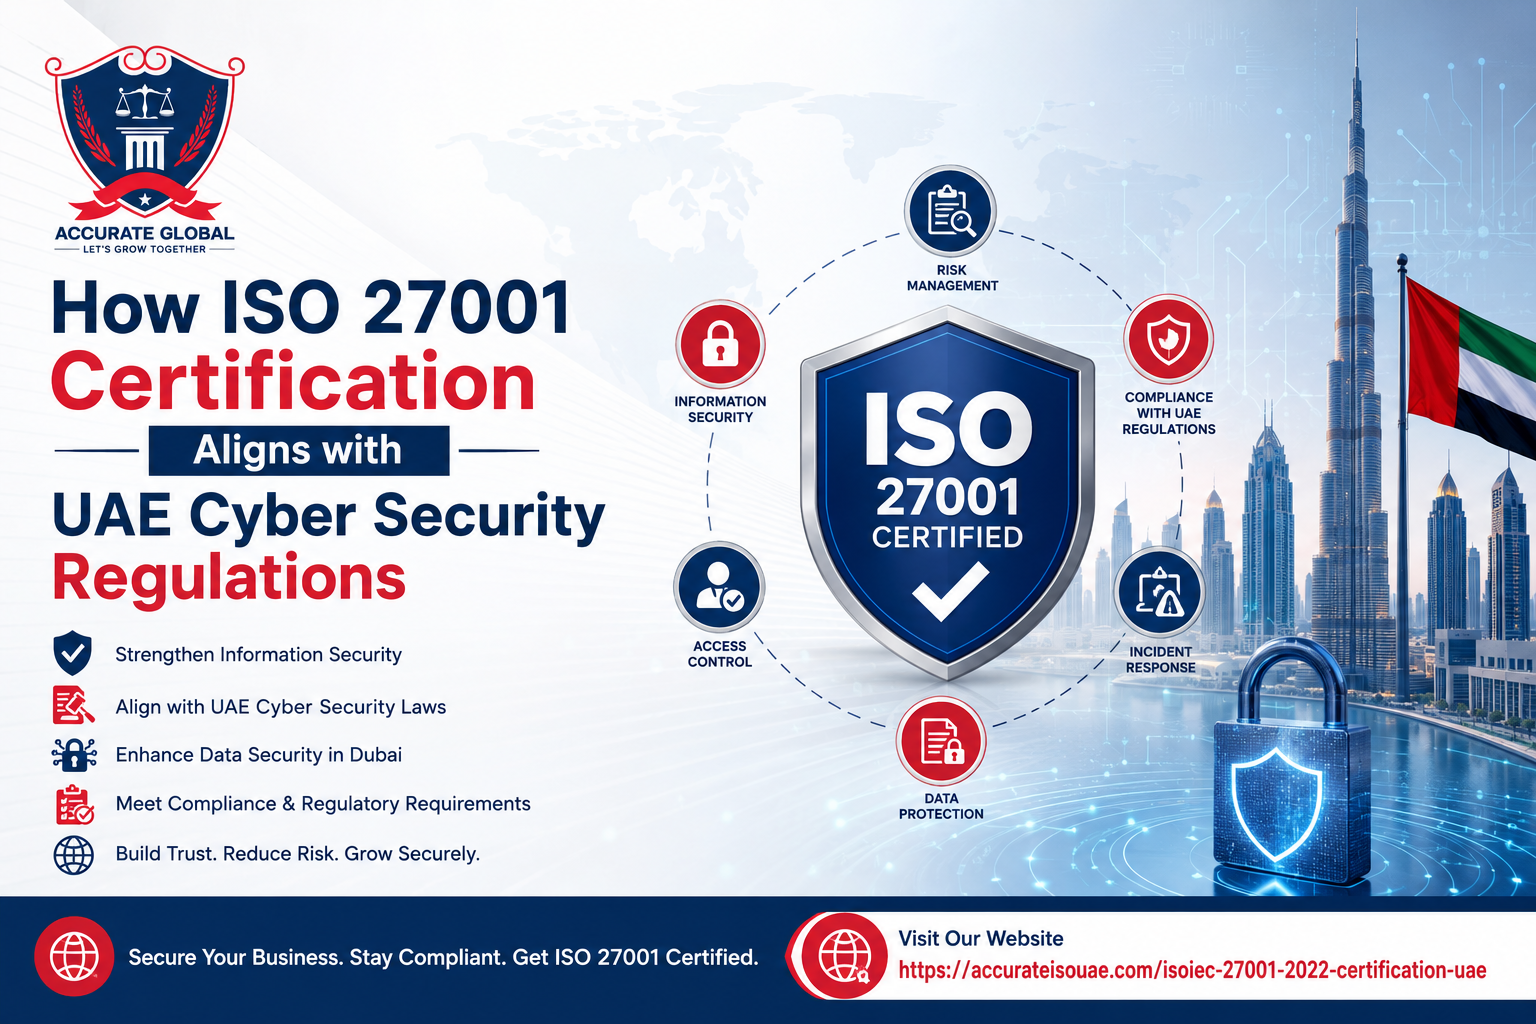
UAE organisations operate under data and cyber expectations such as the Federal Decree-Law on Personal Data Protection and sector or emirate-level information security requirements. ISO 27001 does not replace legal advice, but it provides a structured framework that supports compliance. See how ISO 27001 aligns with UAE cyber security regulations for more.
- Meet vendor security questionnaires from banks, telecoms and enterprises.
- Reduce the risk and cost of data breaches.
- Strengthen tender submissions in IT, finance, healthcare and logistics.
- Create clear roles and accountability for security.
Key Requirements of an ISMS
| Clause Area | What You Must Show |
|---|---|
| Context and scope | Interested parties, boundaries of the ISMS |
| Leadership | Policy, roles, management commitment |
| Planning | Risk assessment, risk treatment, objectives |
| Support | Competence, awareness, documented information |
| Operation | Risk treatment plan implemented |
| Performance evaluation | Monitoring, internal audit, management review |
| Improvement | Corrective action and continual improvement |
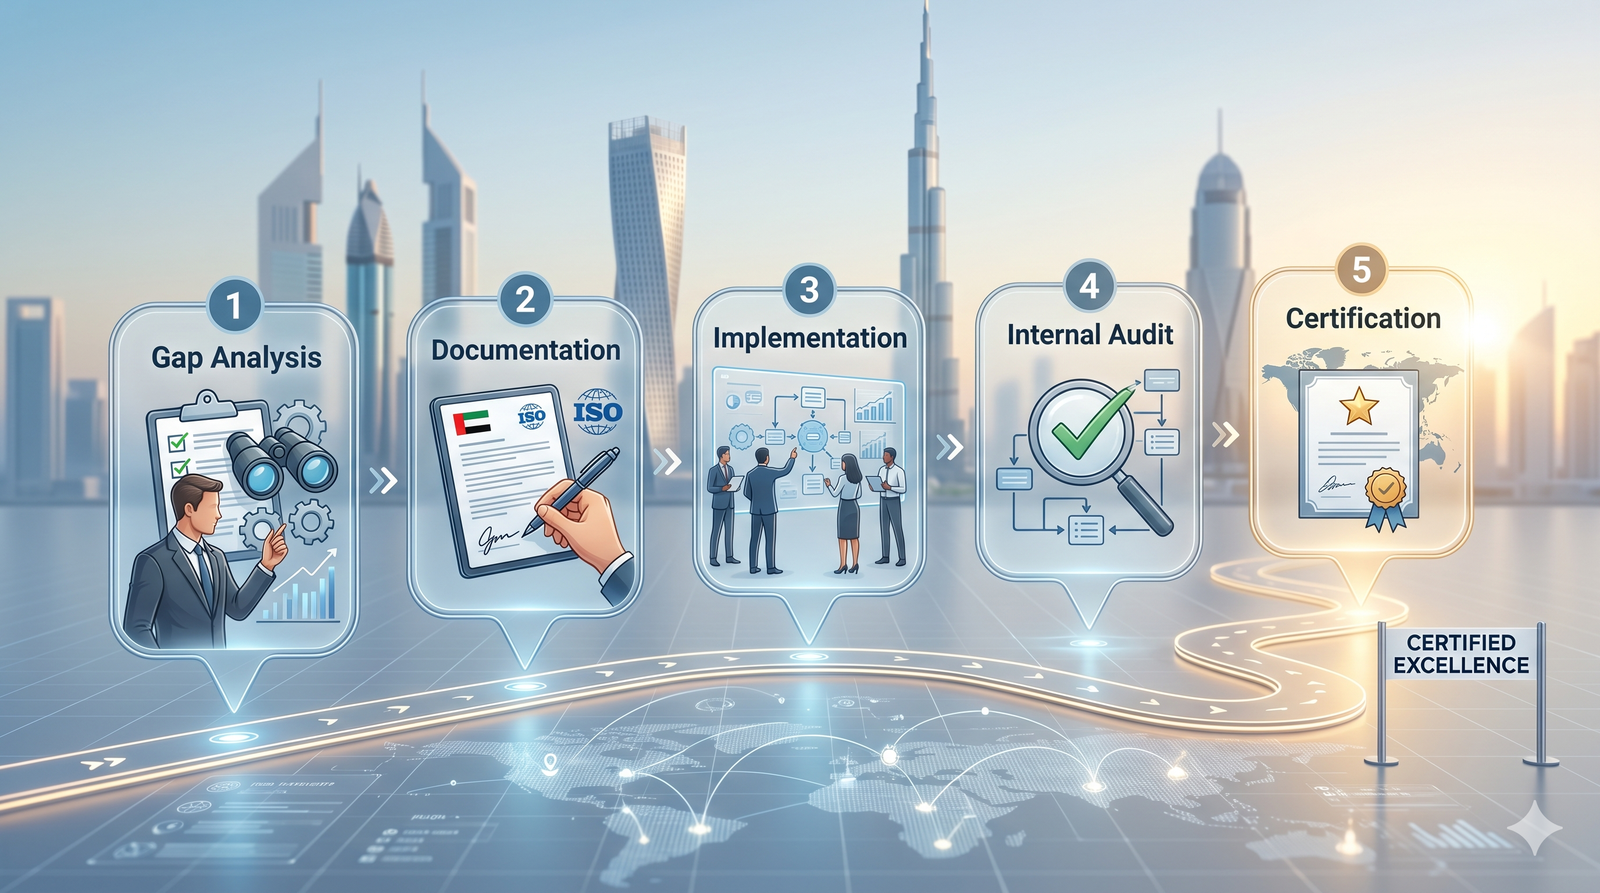
How to Run an ISO 27001 Gap Analysis
- Define scope: departments, systems, locations and data in scope.
- Map current practices: access control, backups, incident handling, vendor management, remote work.
- Compare with the standard: clauses 4 to 10 and the Annex A controls.
- Rate each gap: by risk and effort to fix.
- Create an action plan: owners, deadlines and evidence needed.
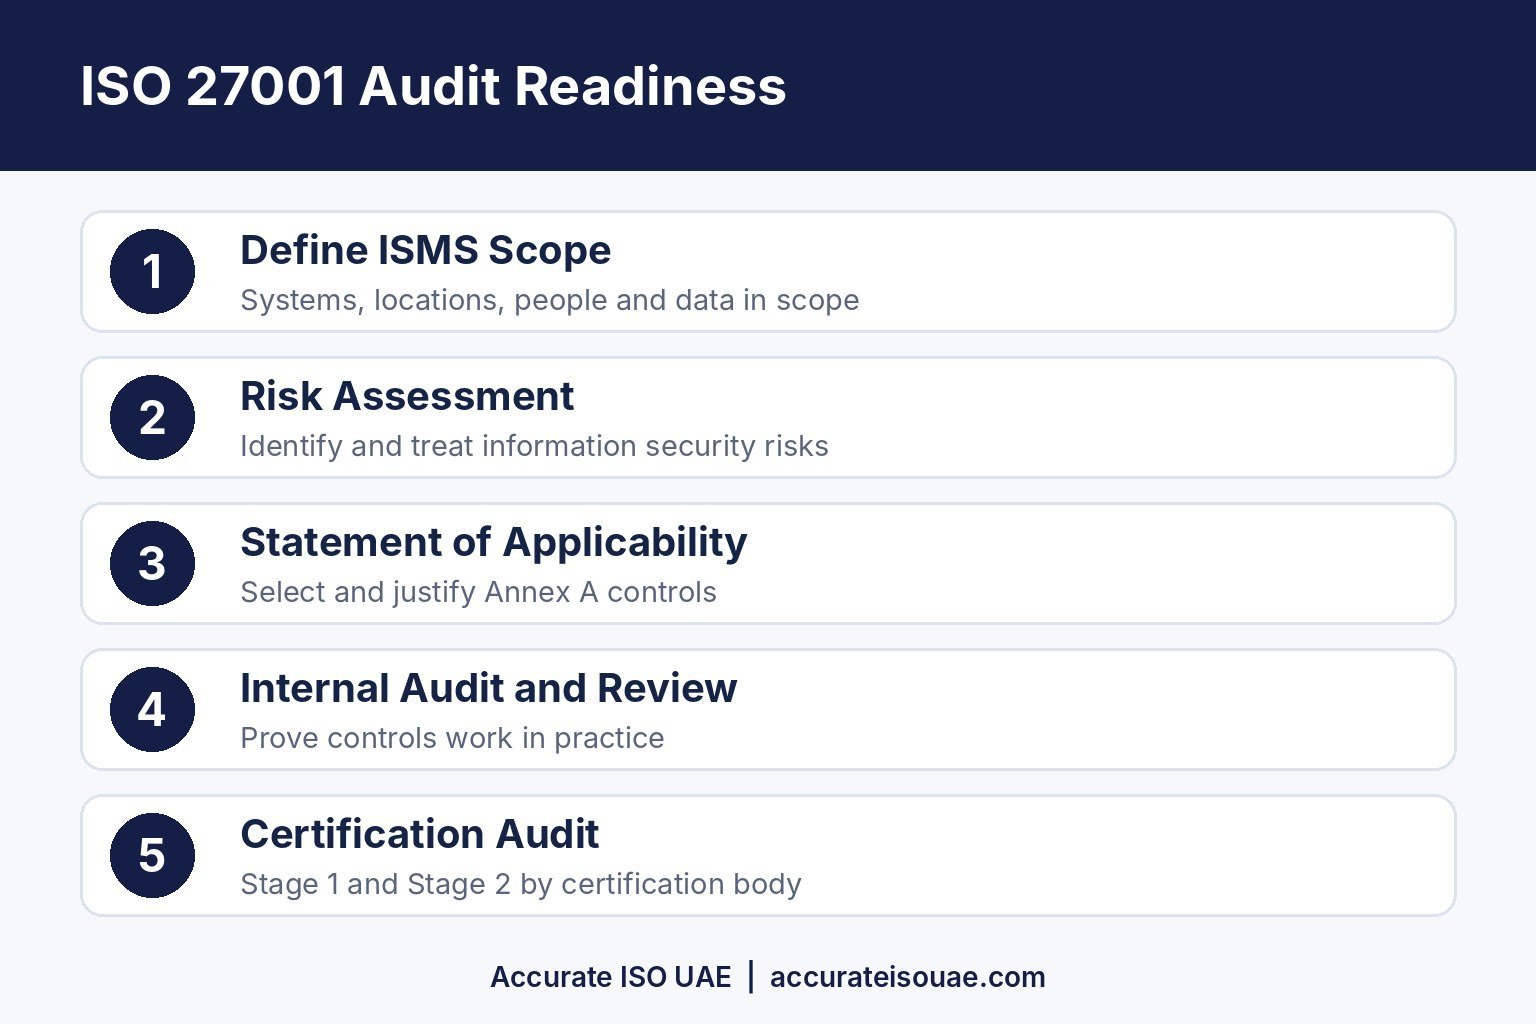
Audit Readiness Checklist
- Approved information security policy and objectives.
- Documented risk assessment and risk treatment plan.
- Statement of Applicability explaining chosen and excluded controls.
- Evidence of staff awareness training.
- Completed internal audit and management review.
- Incident log, access reviews and supplier assessments.
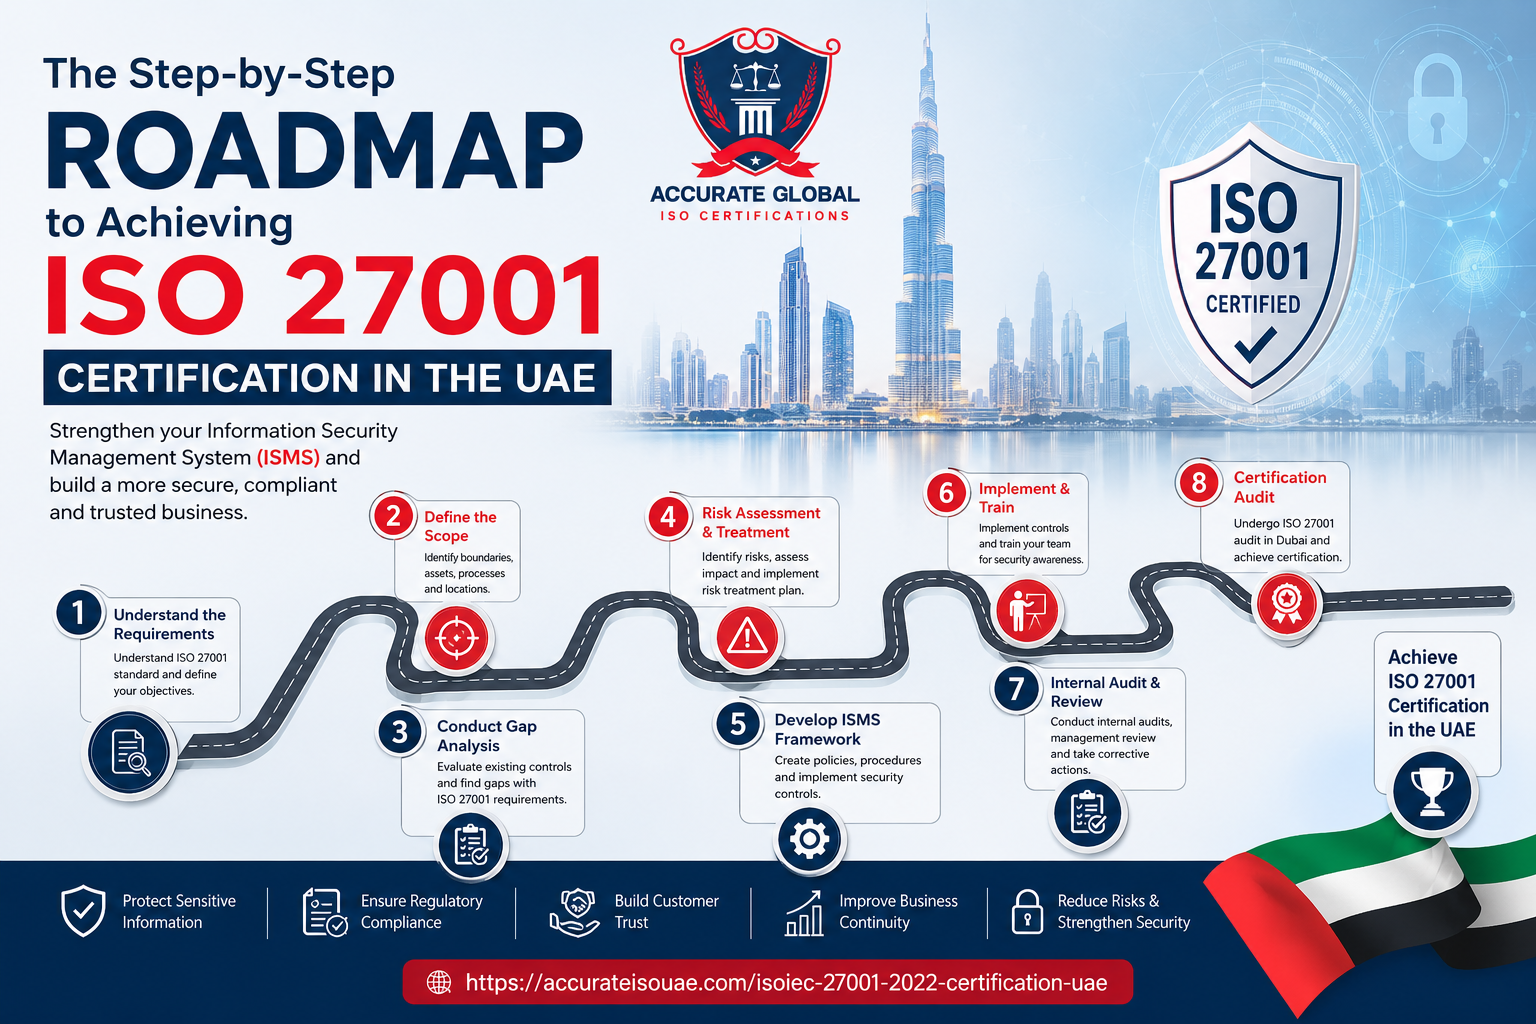
Follow our step-by-step ISO 27001 roadmap for the UAE for the complete process, and see the Stage 1 and Stage 2 audit process guide to understand what auditors review. If you handle personal data, consider adding ISO/IEC 27701:2019 certification.
Common Mistakes to Avoid
- Setting scope too wide on day one.
- Buying tools before understanding risks.
- Writing a Statement of Applicability without evidence.
- Ignoring supplier and cloud risks.
- Skipping internal audit.
Frequently Asked Questions
Is ISO 27001 mandatory in the UAE?
ISO 27001 is voluntary in general, but some customers, tenders and regulated sectors expect it or similar controls.
How long does ISO 27001 compliance take?
Often 3 to 6 months depending on scope, maturity and available resources.
What changed in ISO 27001:2022?
Annex A was restructured into 93 controls in four themes, including new controls such as threat intelligence and secure coding.
Do small companies need ISO 27001?
Any organisation handling sensitive client data can benefit, and a smaller scope can keep the project manageable.
Get Expert Support
Need help with ISO 27001 compliance in the UAE? Speak to our team for a free consultation: call +971 52 315 0586, email info@accurateiso.com or contact our team to request a quote. You can also review our ISO certification prices page to plan your budget.
Related reading: GRC and risk compliance services in UAE.
.png)
.png)
.png)
.png)
.png)
.png)
.png)